Learning path / 06
Agentic DevOps
Your milestone: Investigate it with an agent
Design scoped evidence gathering, reviewed proposals, controlled execution, verification, and evaluation around MicroBank operations.
 Kubernetes
 Git
Before you begin
- Complete Platform Engineering or bring a documented supported workflow, service owner, operating evidence, and recovery path.
- Understand the selected MicroBank profile, GitOps ownership, and the difference between health and transaction verification.
- Begin with offline fixtures; any later controlled execution needs an independent authorization boundary and actual outcome checks.
Your learning progress
0 of 7 available items completed
Back up or restore this path
Progress and notes stay in this browser. A backup contains only this learning path.
The learning sequence
Explore a module to see its bites and proposed checkpoint.
01Bounded agent-assisted operationsProgress from evidence-only work to reviewed and independently checked actions.Available
- Give the agent a bounded jobLearning bite
- Separate facts from hypothesesLearning bite
- Logs cannot grant permissionLearning bite
- Make the proposal reviewableLearning bite
- Approval belongs to one actionLearning bite
- Check the recovered outcomeLearning bite
- Evaluate action and restraintLearning bite
Produce an evidence-linked investigation, exact proposed change, authorization test matrix, verification plan, and evaluation record that includes correct no-change and escalation outcomes.
How to demonstrate this checkpoint
- Show the prediction and the actual observation, with the selected environment or fixture label.
- Meet the stated checkpoint above and retain the verification you used.
- Try the variation in the module’s lesson evidence guide; explain the difference.
- Repeat the original check after any recovery and name remaining unknowns.
MicroBank in this path
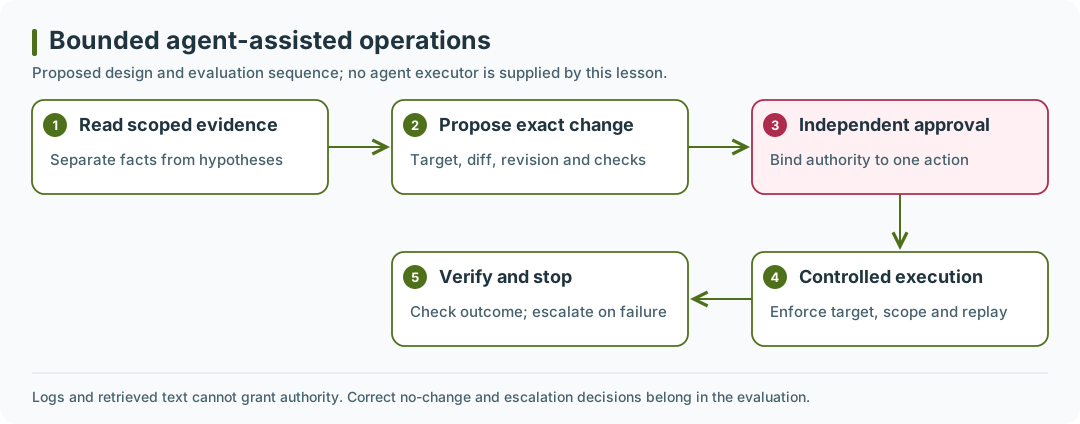
Proposed design and evaluation sequence; no agent executor is supplied by this lesson. Logs and retrieved text cannot grant authority. Correct no-change and escalation decisions belong in the evaluation.
Open the diagram at full size.
Extend a supported workflow
The Platform Engineering path establishes supported developer tasks and their operating boundaries. Its bounded-automation material is the starting point here.
Use MicroBank throughout. In a proposed controlled local scenario, a recorded configuration change sets the Ledger workload to zero replicas. Keep the saved synthetic case and selected application version. The agent reads evidence, distinguishes facts from hypotheses, proposes a narrow restoration to the supported single replica, and stops for independent review.
Keep authority separate from generated text
Read-only tools come first. A proposal does not execute itself. An independent boundary verifies the exact approved actor, target, parameters, revision, expiry, and replay state. Use the established GitOps workflow rather than a new unreviewed deployment path. Verify the same application case after an authorized operation, and stop if the agreed checks fail.
Evaluate before expanding the scope
Include healthy service, stopped Ledger, unavailable database, missing evidence, malicious instructions inside tool output, and replayed approval. Compare the intended decision, actual calls, authorization result, evidence quality, and independently checked application outcome. Record tool calls, time, and model cost with the evaluation.
These are documentation-reviewed design exercises, not a shipped agent runner or verified production integration. The first checkpoint is an offline evidence/authorization/evaluation record. No cloud account or application mutation is needed to complete it.
Related study
Connected learning journey · OWASP AI agent security↗.
Repository ownership
MicroBank↗ owns application code and its application tests. Ship Boring Lab↗ is the selected home for infrastructure as code, configuration management, bootstrap, GitOps, and Backstage configuration: infra/terraform/, infra/ansible/, and gitops/.
Keep ownership explicit. Terraform manages infrastructure resources; Ansible manages host configuration and bootstrap; the selected GitOps controller owns the handed-over Kubernetes desired state. Ansible and GitOps must not continually reconcile the same object. Record the actual repository revision and verification before describing a capability as implemented.
The existing infra/study examples in the pinned MicroBank guides are an isolated course fixture. They remain reproducible reference exercises, not a second authoritative owner for the operating platform. Adopt the relevant configuration into Ship Boring Lab deliberately, with separate state and a reviewed ownership handoff.